About
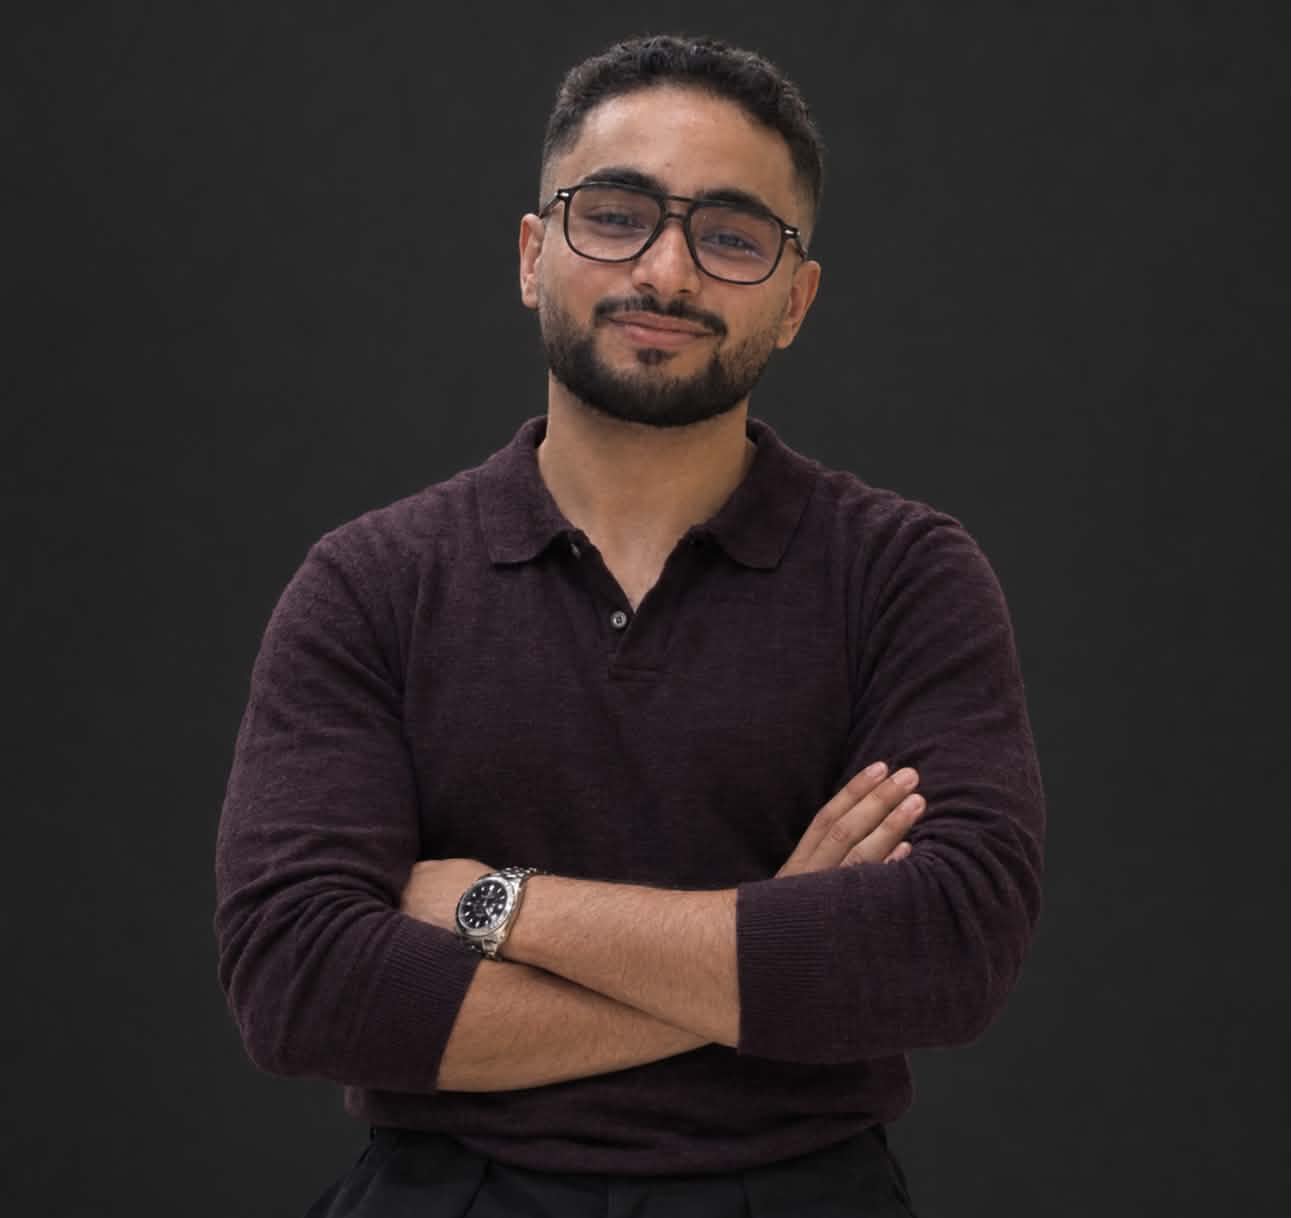
I’m Aziz, Pulgaa online. I study software engineering at INSAT and work on the investigation side of security: forensics, incident response, malware analysis and reverse engineering.
I take compromised systems apart, from memory dumps and disk images to packet captures, and rebuild what the attacker did, step by step. When the trail leads to a binary, I reverse it, from an XWorm RAT’s encrypted configuration to a tampered UEFI loader. In the past year that meant 1st in Tunisia at Securinets CTF Quals 2026, 1st at the Advanced Cybersphere CTF, a summer internship at DefensyLab, and teaching forensics at Securinets INSAT, where I also write challenges for the club’s CTFs.
I’m looking for internships and roles in incident response, detection engineering, malware research or reverse engineering.
- Focus
- Forensics & IRMalware & reversingDetectionOffensive tooling
- Stack
- PythonGoVolatilityGhidraSplunkWazuhIDA ProBurp Suite
Background
Software Engineering
National Institute of Applied Science and Technology, where I built my foundation in software engineering and systems architecture.
- 15+ modules across networking, operating systems and programming
- Top 10% in core computer science subjects
Where security started
Self-taught defensive security alongside the engineering curriculum, then a habit that never stopped.
- Top 1% globally, out of 3M+ users
- 100+ rooms on DFIR, malware analysis and threat intelligence
- SOC Level 1 path completed in 2025: Splunk, YARA rules and Sysmon log analysis
Cybersecurity Professional Certificate
8 courses on SIEM tools, incident response and Linux security, finished in under 3 months.
University security club
Joined Securinets INSAT as a member and took part in 5+ internal trainings on web exploitation and forensics, before moving on to the technical teams.
Experience
-
Securinets INSAT
2026 – PresentTechnical Team Instructor
Teaching DFIR and forensics to club members, mentoring newcomers through hands-on labs, and writing challenges for the club’s events, including part of the Friendly Securinets CTF 2026.
-
DefensyLab
Summer 2026Defensive Security Research Intern
Built a platform that checks whether real CVEs in an organisation’s own software are actually exploitable, and whether the SOC detects them. Each finding is reproduced in a disposable, network-isolated sandbox behind human approval gates, monitored with Wazuh.
Read the project -
Securinets FST
2026Technical Team Member
Led forensics workshop sessions for 30+ club members and coordinated logistics for the club’s CTF events.
-
Team MOJO-JOJO
2025CTF Player & Challenge Author
Core player in national and international competitions, focused on forensics. Authored 4 original forensics challenges used in competitive CTF events.
Achievements
-
1st
Writeups
Securinets CTF Quals 2026
Oct 2026 · 1st in Tunisia · 3rd in the MENA region
-
Top 3
Darkest Hour 2026
2026
-
1st
Advanced Cybersphere CTF
First place
-
Top 10
Writeups
Cybertek CTF 2026
Apr 2026
-
1st
Writeups
QnQSec CTF 2025
Oct 2025 · first place
-
Top 7
Securinets National Finals
2025
-
38th
Writeups
Securinets CTF Quals 2025
International · 5th in North Africa · with Team Mojo Jojo
Milestones
Recent posts
Full blog- WriteupSecurinets Quals 2026 Silent Tone Three radio transmitters talk over each other on one 433 MHz channel. Read the protocol out of a USB log, repair a logic-analyser recording that silently dropped samples, decode the loud decoy, subtract it, and peel the two quiet transmitters apart to rebuild an encrypted flag. Hard 35 min
- WalkthroughSep 2026 Memory Forensics with Volatility 2 & 3 A complete memory forensics guide: Volatility 2 vs Volatility 3 and when to use each, installation, acquisition, and a full Windows investigation workflow with side-by-side commands for processes, network, injection, files, registry, credentials, timelines, and Linux memory. 37 min
- WriteupFriendly Securinets CTF 2026 Forensics Wave 1 Seven easy-to-medium forensics challenges: header repair, layered encodings, nested archives, a disguised shell archive, low-contrast stego, Morse audio, and a PNG/PDF polyglot. Easy 13 min
Open to security roles
Internships and full-time positions in incident response, detection engineering, malware research or security tooling, or a CTF team that needs another player.
azizhaddadi10@gmail.com